Know what you're protecting, what threatens it, and what to fix first.
Independent, senior-led security consulting for organizations that need a clear, defensible picture of their risk. Every engagement is run by a practitioner with more than 25 years in Canadian and international federal security, not handed to a junior analyst.
Threat and Risk Assessments
Structured TRAs using recognized methodologies, including the Harmonized TRA (HTRA). We identify assets, threats and vulnerabilities, rate residual risk, and give you prioritized recommendations you can act on and defend.
Physical Security Reviews
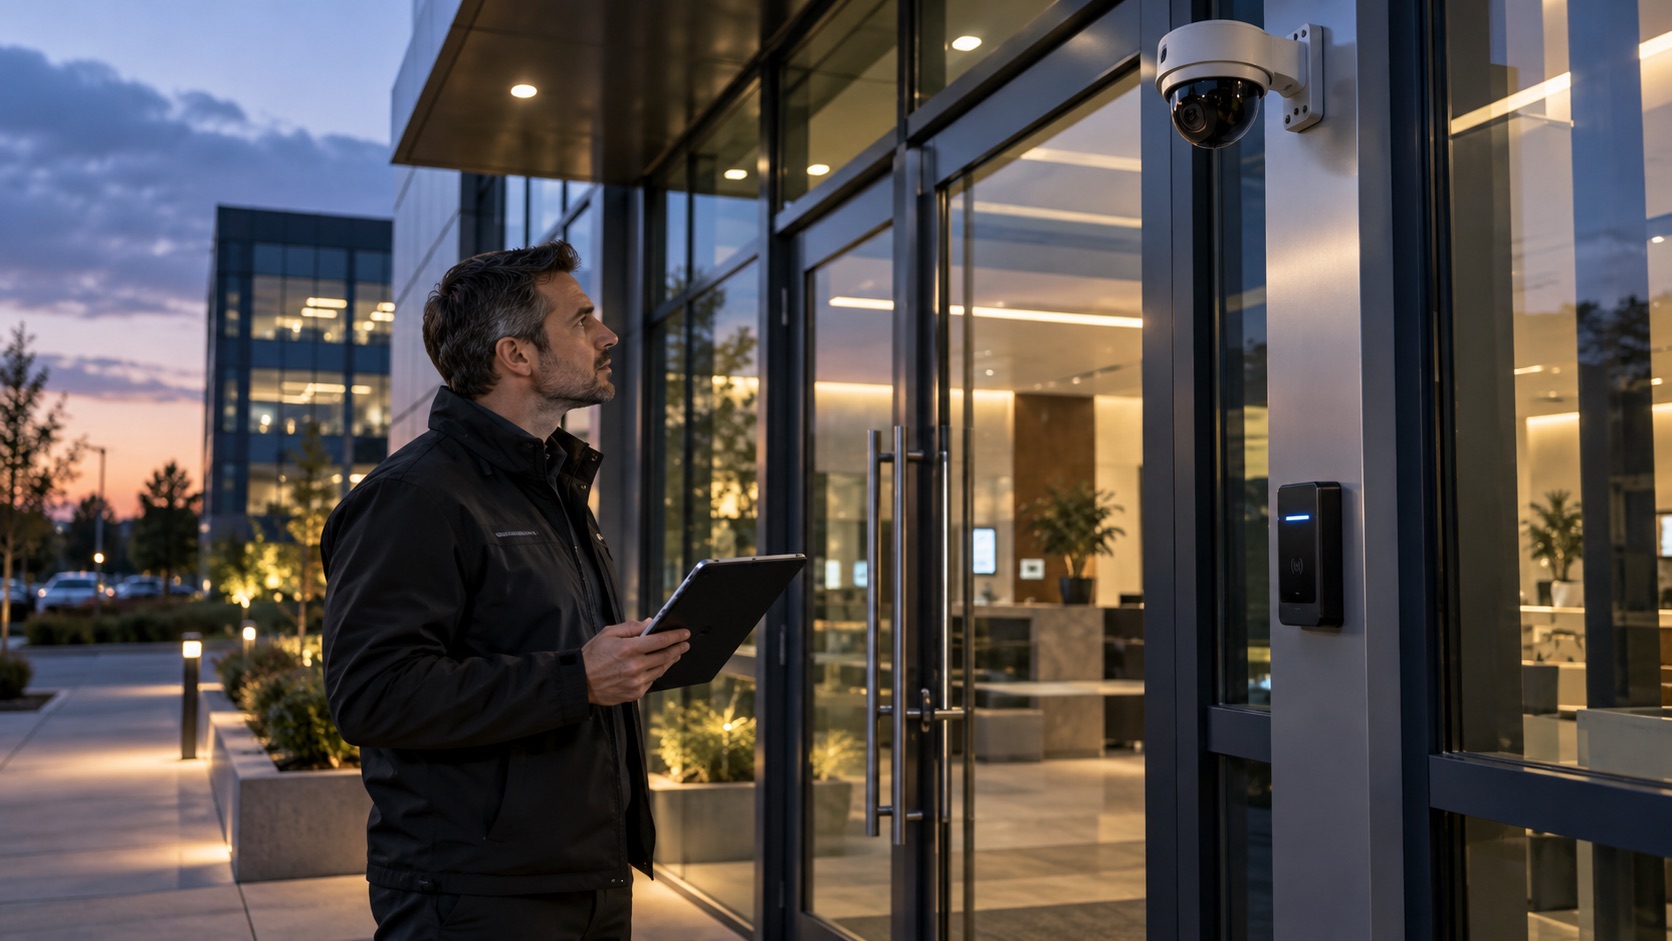
Site walk-throughs of perimeters, access control, lighting, CCTV coverage and guard posts, with findings tied to real-world threats rather than a generic checklist.
Security Policy & Standards
Policies, procedures and standards written to fit how your organization actually operates, so they get followed rather than filed.
Security Program Design
A roadmap from where your security program is today to where it needs to be, with phases, owners and costs.
Investigations Support
Experienced support for internal investigations and incident reviews, from scoping to a clear written account of what happened. See Investigations & Screening for our software-backed services.
From a list of worries to a ranked plan.
Each threat is rated by likelihood and impact against your current safeguards. The result is a clear picture of which risks need action now, which can wait, and which you can accept.
We work with recognized methodologies, including the Harmonized Threat and Risk Assessment (HTRA), and match the approach to your organization and its stakeholders.
- T-0112Tailgating at staff entrance
- T-0212Unmonitored loading dock
- T-0310Insider data removal
- T-0420After-hours intrusion
- STEP 01
Scope
Agree on the assets, sites and questions that matter, and what a useful result looks like.
- STEP 02
Assess
Interviews, document review and site visits to understand threats, vulnerabilities and existing controls.
- STEP 03
Analyse
Rate each risk by likelihood and impact, and test current safeguards against it.
- STEP 04
Recommend
A prioritized, costed plan, presented to the people who need to act on it.
- Organizations without an in-house security team
- Property and facility operators
- Boards and executives who need an independent view
- Security teams that need a second set of eyes
AI for Security Firms
→AI automation built by someone who knows security work: reports, proposals, scheduling and calls.
Government & Defence
→Federal security experience, TRAs and software-backed personnel screening for departments, defence and contractors.
Investigations & Screening
→Open-source investigations and personnel security screening, backed by our own software.
Start with a confidential conversation.
Tell us what you're protecting and what's worrying you. You'll speak directly with the founder, not a sales team.